
Cathedral Cyber is a small, veteran-owned red team and penetration testing consultancy for DoD and federal clients. We find the gaps before your adversaries do.
>_ About
Mission, not marketing
The best way to defend against sophisticated adversaries is to think like one.
Cathedral Cyber is a veteran-owned red team and penetration testing consultancy built for DoD and federal clients who need clarity, not compliance theater. We don't sell fear. We sell clarity. We mirror how real adversaries think and move, so your defenders get a realistic training ground and your leadership gets an honest picture of resilience.
Our approach is simple: if your security can't withstand an adversary who thinks like you, it won't survive one who doesn't. We operate from the inside out — understanding your mission, your constraints, your threat model — then testing your defenses the way a real attacker would. No scripts. No checklists. Just adaptive, intelligent pressure.
We also build tools. The same mindset that breaks systems can harden them. Our research in continuous integrity monitoring, adversary simulation, and deployable red team infrastructure feeds directly into every engagement — giving you access to capabilities that exist nowhere else.
>_ Research Foundation
Cathedral Cyber's methodology is grounded in peer-reviewed research. Our founder served as Principal Investigator on the NISE-funded HELICS research effort at NIWC Pacific; the foundational work is published on DTIC (Technical Document 3429, 2024). We don't just test. We advance the state of the art.
Clearance
TS/SCI Eligible (Previously Held)
Certification
OSCP
Status
100% Veteran-Owned
>_ Founder
James Allphin
26 years of offensive operations. One mission: make defenders better.
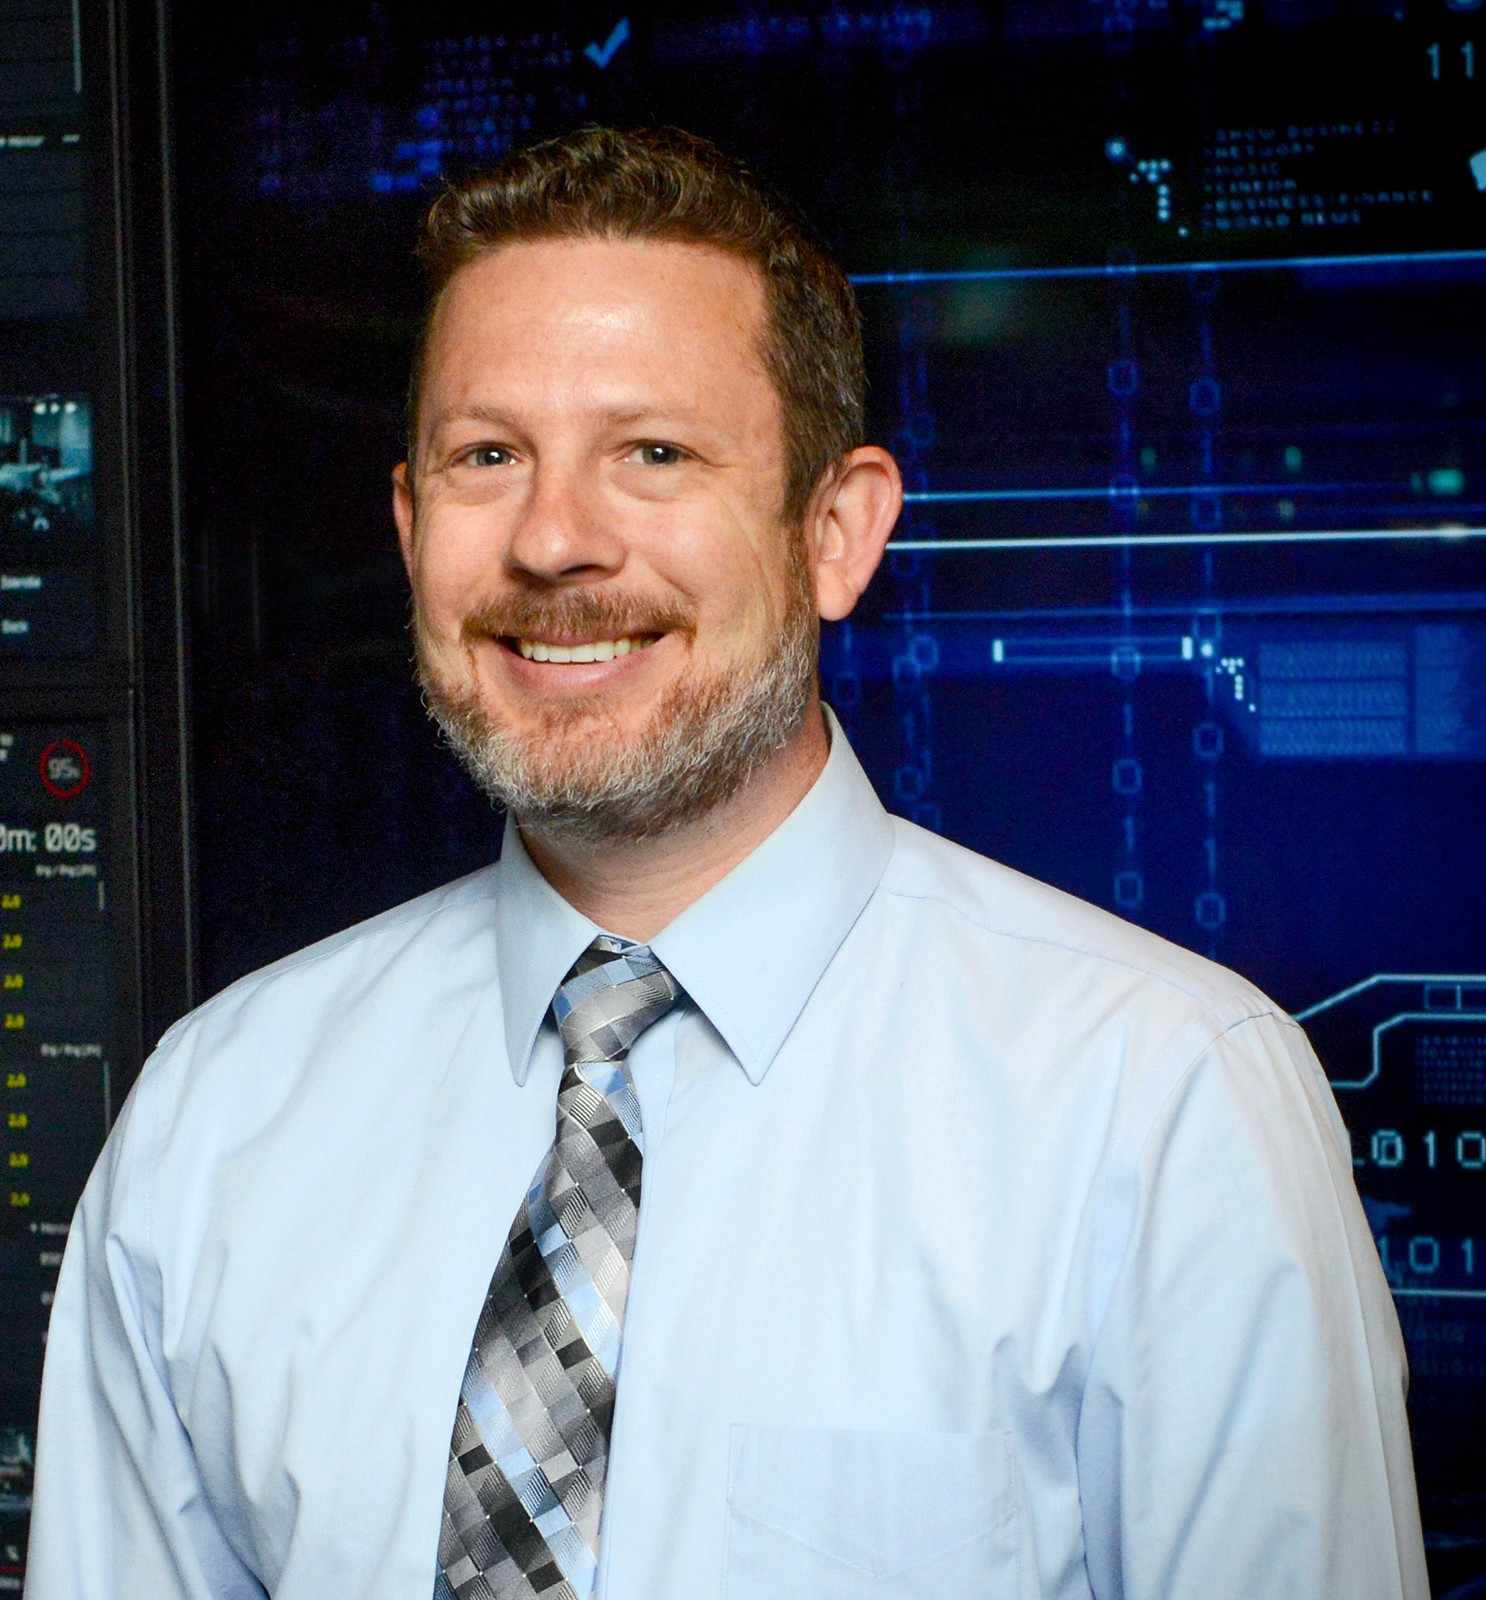
I've spent 26 years breaking into the things you're trying to protect. At NIWC Pacific, I served as Chief Hacker and Senior Penetration Tester, leading red team operations against the DoD's most critical systems — from warship LAN lockers to SOCOM programs. I've operated in the places that don't make it onto resumes.
But I didn't just want to find vulnerabilities. I wanted to understand why they persist. That led me to found the Cyber White Paper Working Group at NIWC Pacific, where HELICS was born. I served as Principal Investigator and lead author on the NIWC Pacific research team for the NISE-funded effort that engineered and prototyped HELICS — a blockchain-based integrity monitoring system that proves what changed on a system and when. The foundational research is published on DTIC (TD-3429, 2024); the patent is in stage 2 of 3.
Cathedral Cyber is the culmination of that dual perspective: a veteran-owned red team and penetration testing consultancy built for DoD and federal clients who need clarity, not compliance theater. We think like adversaries, build like engineers, and test like your mission depends on it — because it does.
>_ Capabilities
What we do
Six disciplines. One adversarial mindset.
Red Team Operations
Full-scope adversary simulation against live environments. We play the role of your most capable threat.
Penetration Testing
Network, application, and physical assessments. Scoped engagements with actionable reporting.
Compliance Gap Assessment
CMMC and NIST 800-171 gap assessments. We identify control failures; your team owns the remediation and RMF package.
Threat Modeling
Identify your highest-value targets before an adversary does. Architecture review and kill-chain mapping.
Security Architecture
Design review for systems built to resist nation-state-level persistence and lateral movement.
Training & Workshops
Hands-on red team operator training. Purple team exercises. Detection engineering workshops.
>_ Arsenal
Tools forged in the field
Tooling developed during live engagements.
Passive shell session capture
Transparent PTY wrapper that timestamps every keystroke to SQLite. AI synthesis clusters activity by target and phase, maps to MITRE ATT&CK, and exports structured findings. Renaming to Raziel (raz CLI) — coming soon.
Deployable nerve center
Portable Docker-based red team server. Matrix Synapse, Covenant C2, IVRE, Gitea, CyberChef, Nextcloud — deploy, operate, destroy.
Blockchain-based integrity monitoring
Tamper-evident system baselines using distributed ledger technology. STIG compliance fingerprints anchored to blockchain — proving what changed, when, and by whom. Research-backed, field-tested.
Evasive payload tooling
Private collection of Cobalt Strike scripts, BOFs, profiles, and evasive payload tooling developed for authorized red team engagements.
>_ Establish Contact
Engage
Tell me what you're defending. I respond within two business days.
Transmission logged
Your inquiry has been prepared. We'll respond within two business days.